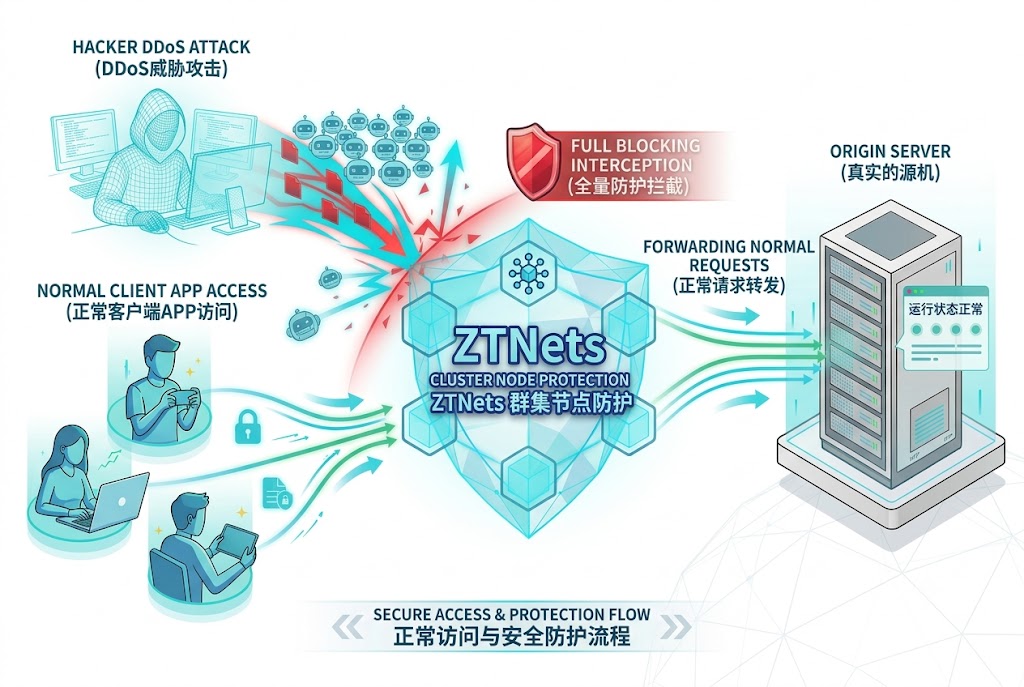
Shield your backend servers from public exposure. ZTNets provides SDK-based Zero Trust security and TCP/UDP dynamic acceleration for mobile, desktop, and API infrastructure.
Built from the ground up for applications that cannot afford downtime, exposure, or latency.
Absolute source server invisibility
Never expose your real IP. Your backend infrastructure stays completely invisible to public scans, DNS enumeration, and targeted attacks. Your origin simply does not exist on the public Internet.
Kill attacks at the endpoint
Client-side SDK verification eliminates malicious automation at the device level before it ever reaches your network. Device fingerprinting, behavioral analysis, and cryptographic challenge-response ensure only real users connect.
Full-protocol dynamic routing
Multi-path dynamic routing instantly bypasses Internet congestion, cutting latency and packet loss for global users. Our SDK optimizes the "last mile" from client to edge—something traditional CDNs simply cannot do.
Deploy without touching servers
No complex firewall rules, no server reconfiguration, no BGP announcements required. Simply integrate our lightweight SDK into your client application and your entire backend is protected instantly.
See why modern infrastructure teams are moving away from legacy high-IP and CDN-based defenses.
| Capability | Traditional High-IP / CDN (BGP / Anycast) |
ZTNets AppShield (SDK Mesh) |
|---|---|---|
| Origin IP Protection |
Vulnerable
Easily exposed via DNS leaks, historical records, or direct subnet scanning |
100% Hidden
Physical concealment — origin is completely invisible on the public Internet |
| CC / Bot Attack Defense |
High False Positives
Relies on IP rate limiting; cannot stop residential proxies or sophisticated bots |
Zero False Positives
Device fingerprint + behavioral verification at the endpoint — precision filtering |
| TCP / UDP Acceleration |
Partial
Only datacenter-to-datacenter; cannot optimize the client "last mile" |
Full Path
SDK-side multi-path with dynamic packet loss recovery on the client edge |
| Client-Side Protection |
None
Client has no awareness; cannot defend against protocol reverse-engineering |
Full SDK Shield
Memory protection, encrypted transport, multi-layer signature verification |
| Deployment Complexity |
Complex
Requires DNS cutover, BGP announcements, firewall rules, and server config |
10 Minutes
Drop SDK into your app, configure rules in console — zero server changes |
From zero to fully protected in under 10 minutes. No infrastructure changes required.
Drop our lightweight SDK (<2MB) into your iOS, Android, Windows, or macOS application. Available via CocoaPods, Maven, NuGet, and npm.
Configure your origin server ports, forwarding logic, and security policies on the ZTNets Cloud Console. Visual rule editor with instant preview.
Traffic routes through our ultra-low latency global edge network. Your backend is now 100% protected and accelerated. Monitor everything in real-time.
A streamlined onboarding flow from purchase to production.
Purpose-built security and acceleration for the most demanding network environments.
Shield matching engines and WebSocket APIs from DDoS attacks that spike during volatile market movements. Ensure zero interruption when it matters most.
Withstand T-level DDoS attacks while solving cross-region latency and packet loss for real-time multiplayer and voice chat.
End-to-end encrypted transmission at wire speed. Prevent order interception and front-running during high-concurrency trading events.
Replace legacy VPNs with a software-defined perimeter. Employees access internal resources securely without exposing your corporate network.
Start free, then scale as your device fleet grows. No hidden egress fees.
Try the full platform with zero commitment.
Perfect for early-stage apps and small fleets.
For growing products with larger user bases.
Enterprise-grade protection at global scale.
Need a custom enterprise plan? Contact sales for SLA-backed pricing and dedicated onboarding.
Get 14 days of full-featured free trial. No credit card required.